Security leadership. Technical depth.

Nathan Joyce.

Information Systems Security Manager

Security clearanceTS/SCI FSP

Whitman, Requardt and Associates · Sep 2024 — Present

I connect the details inside a network with the decisions that protect it. My work brings together security engineering, risk management, and intelligence.

1,100+Users reached

100+Critical vulnerabilities

ATOWithout deficiencies

Draper, Utah / Federal · Defense · Private sector
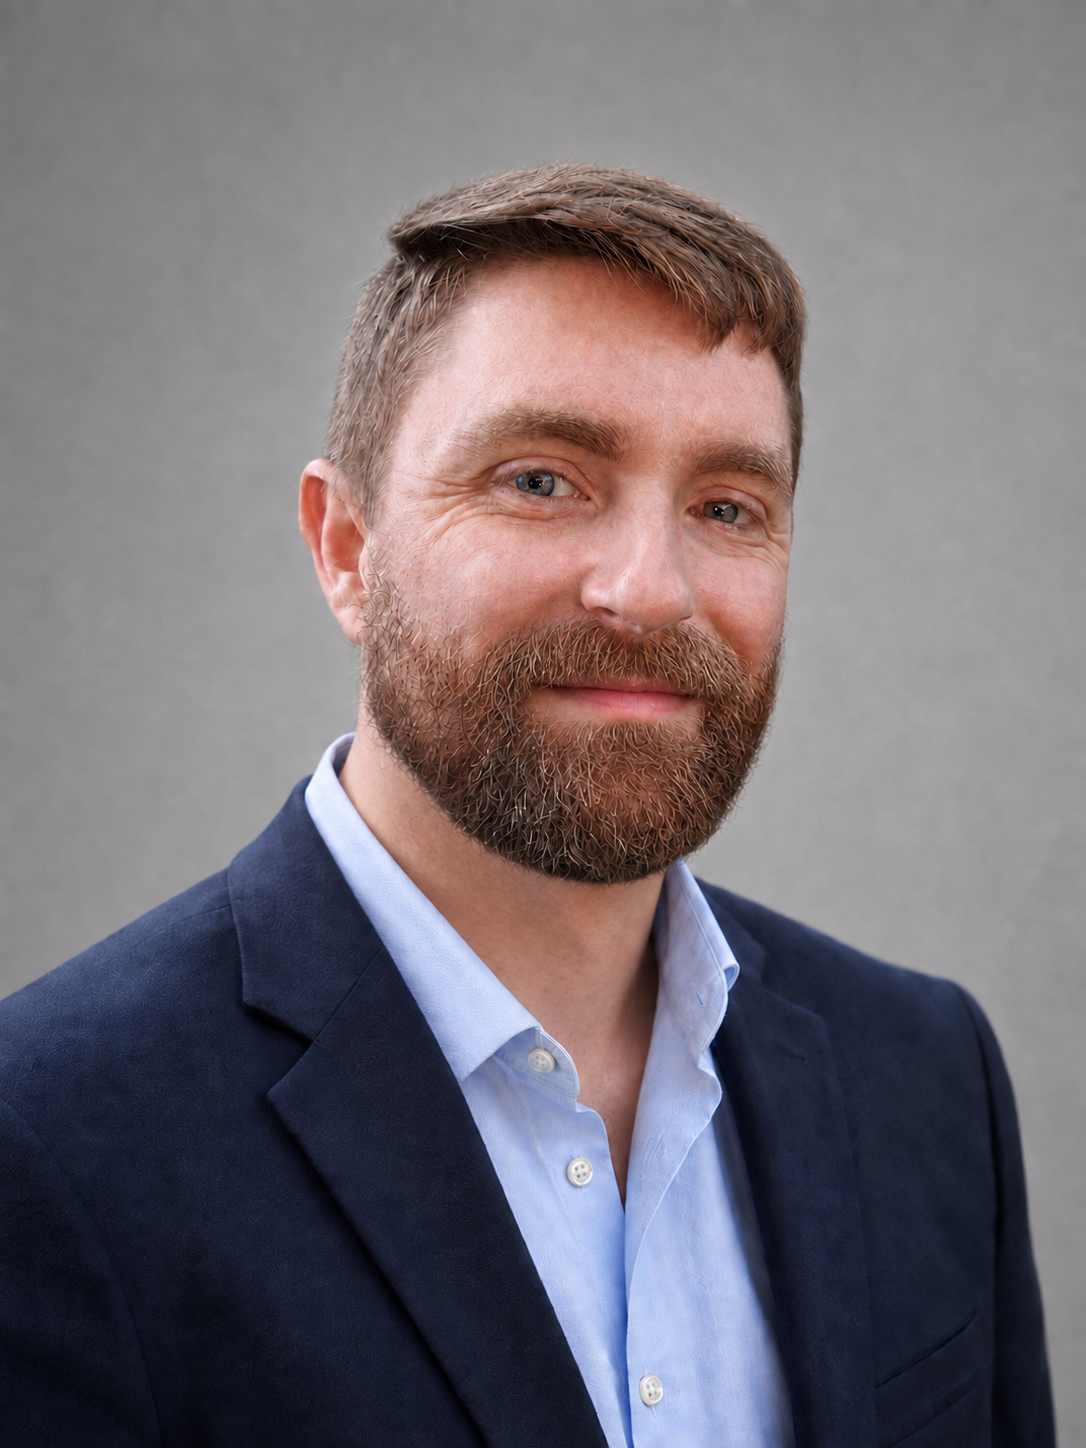
Portrait of Nathan Joyce
Nathan JoyceSecurity leader & independent builderDraper, Utah

Experience across mission-driven organizations

The work I do

Strategy informed
by hands-on experience.

From network behavior to executive briefings, I work across the technical and organizational sides of security.

Security programs
& assurance

Build defensible security programs, translate requirements into controls, and prepare systems for authorization and assessment.

  • Risk Management Framework
  • CMMC & NIST 800-171
  • NIST 800-53 & system security plans
  • Provider & stakeholder coordination
See leadership experience

Engineering
& vulnerability analysis

Understand how systems behave, validate weaknesses, and make remediation practical for the people who run them.

  • Network & systems hardening
  • DISA STIGs & CIS Benchmarks
  • Penetration testing
  • Configuration automation
See engineering experience

Intelligence
& incident response

Connect network activity, threat context, and evidence into clear findings that support operational decisions.

  • Cyber intelligence & SIGINT
  • Target network analysis & OSINT
  • SIEM & threat monitoring
  • Response coordination & briefings
See intelligence experience

Selected contributions

The work, in practice.

1,100+

Users reached

Security awareness campaigns designed and executed through KnowBe4 at WRA.

Security leadership

100+

Critical vulnerabilities

Identified and helped remediate across client engagements with InFocus Consulting.

Penetration testing

Independent projects & agentic development

Security instincts.
A builder’s mindset.

Alongside my security career, I’m developing VidarFit and exploring how AI agents can support the full software lifecycle: research, design, implementation, testing, and release.

Featured project · Early access

VidarFit

Adaptive strength training, built around the athlete.

I’m building a training product that turns a person’s goals, equipment, recovery, and workout history into an adaptable plan.

  • Personalized sessions and multiweek programs
  • Recovery-aware training and progress tracking
  • Exercise, nutrition, and group-training tools
  • Visible reasoning and user control over the plan
VidarFit product artwork with its V emblem
Independent product developmentFrom a training idea
to a working application.

Side project · Playable now

BlockCraft Math

A 3D block-world math adventure for 3rd graders.

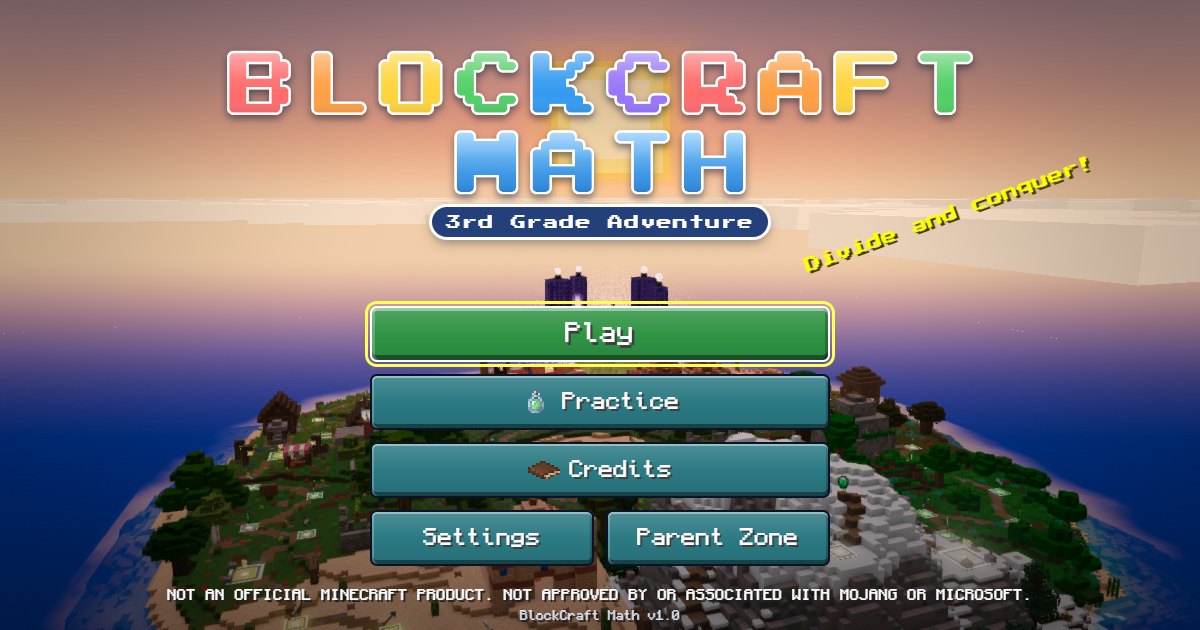
A browser game I built with AI coding agents. Kids practice third-grade math by battling mobs, mining ore, building farms, and trading with villagers across a story campaign.

  • All 28 Grade 3 Common Core math skills
  • Adaptive difficulty with hints and read-aloud
  • Step-by-step explanations after a wrong answer
  • Runs entirely in the browser, no account needed
  • First-person VR edition for Meta Quest 3

NOT AN OFFICIAL MINECRAFT PRODUCT. NOT APPROVED BY OR ASSOCIATED WITH MOJANG OR MICROSOFT. BlockCraft Math is a free, fan-made game. The preview image shows textures from Pixel Perfection by XSSheep and Nova Wostra (via Mineclonia), CC BY-SA 4.0, adapted.

BlockCraft Math title screen over a blocky island at sunset
Game development with AI agentsMath practice that
feels like an adventure.

Side project · Playable now

Uplink: Network+ VR

A virtual-reality network operations center that teaches CompTIA Network+.

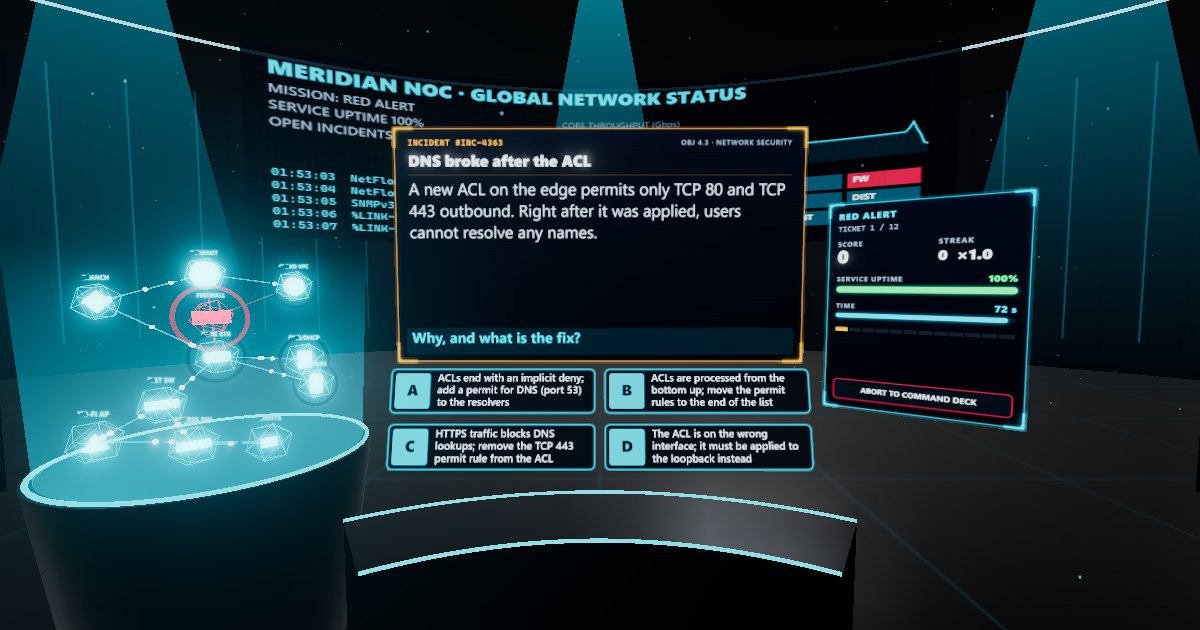
A WebXR training game I built with AI coding agents. Players answer scenario tickets at a NOC command console, then teleport to a lab bay to rack virtual gear, console into a simulated switch and router, and troubleshoot a broken network.

  • 91 original scenarios across all five N10-009 domains, plus a 30-ticket run weighted like the exam
  • Lab 1: mount a rack, choose optics and cables, power it up
  • Lab 2: a simulated IOS-style command line for VLANs, trunks, routing, DHCP and PAT
  • Lab 3: break-fix with show commands and a cable tester
  • Meta Quest controllers or hand tracking, mouse and keyboard, or touch

Not affiliated with, sponsored by or endorsed by CompTIA or Cisco. CompTIA and Network+ are trademarks of CompTIA, Inc.; Cisco and IOS are trademarks of Cisco Systems, Inc. Scenarios are original practice material, not exam questions.

Uplink network operations center with an incident ticket, four answer choices and a glowing network topology hologram
WebXR game development with AI agentsCertification study
inside the NOC.

How I work with agents

Direct. Iterate.
Verify.

Research & specify

Give the work a clear purpose.

Use research, written requirements, and persistent project context to turn broad ideas into concrete work for AI coding agents.

Build & challenge

Iterate across perspectives.

Work with Codex and Claude Code on implementation, debugging, design, and review, refining the result through repeated feedback.

Test & release

Check the result in the real product.

Connect automated tests, browser verification, version control, and Cloudflare deployment into a practical development workflow.

1,099GitHub commit contributions2026 year to date
1,616VidarFit codebase commitsDefault-branch history · all authors
≈42.9BRecorded AI token usageIncludes cached input · local logs
About these numbers

Snapshot: September 5, 2026. GitHub reports 1,099 commit contributions associated with my account from January 1 through September 5. VidarFit’s codebase contains 1,616 commits in its default-branch history, including work produced with agents and any other authors. These are different measures and are not added together.

Token usage: approximately 42.9 billion tokens recorded in available local Codex and Claude Code session logs from July 15 through September 5, 2026. This includes input, generated output, and cached-input processing. Most of the volume is cached input; it is not 42.9 billion tokens of newly generated text, a billing total, or a complete lifetime ledger.

The estimate deduplicates repeated Codex usage events and Claude message IDs. Local logs are incomplete across providers and machines, so this is an activity estimate with a defined scope.

Read the snapshot data

More of the learning journey

Public repositories include research reporting, interface experiments, and practical applications.

View my GitHub

Professional experience

A career built
across perspectives.

Security leadership, consulting, engineering, and military service. Explore each role for responsibilities and technical detail.

2024 — PresentSecurity leadership
Current role

Information Systems Security Manager

Whitman, Requardt and Associates

Sep 2024 — Present

Leading information assurance and network security across multiple enclaves, connecting technical controls with authorization, assessment readiness, and incident response.

  • Achieved authorization to operate without deficiencies through end-to-end Risk Management Framework activities.
  • Built the enclave System Security Plan and supporting evidence for NIST 800-171 and CMMC assessment readiness.
  • Designed security awareness campaigns for 1,100+ users and all cleared personnel.
View full role details8 areas of responsibility & technical workExpand

Assurance & authorization

Lead information assurance and network security programs for multiple information systems, driving end-to-end RMF activities across multilevel network enclaves.

Assessment readiness

Implement NIST 800-171 controls and CMMC requirements, coordinating with managed security and service providers to develop the enclave SSP and supporting artifacts.

Vulnerability analysis

Use Nessus and SCAP benchmarks to assess enterprise configurations and system architectures, identify security gaps, and drive remediation across federal and state contracts.

System hardening

Apply DISA STIGs and CIS Benchmarks to network devices and servers. Develop custom hardening strategies for systems that lack formal guidance.

Detection & response

Integrate Arctic Wolf, Splunk, Windows Defender, and Palo Alto Cortex to centralize network analysis and support incident detection across multiple enclaves.

Incident leadership

Author the corporate Incident Response Plan and coordinate cross-functional response, external forensics, legal engagement, real-time timelines, and executive briefings.

Security awareness

Design and execute KnowBe4 campaigns for 1,100+ users and all cleared personnel to support secure enterprise network use.

Network understanding

Analyze and map enterprise enclaves, traffic flows, and misconfigurations to support red-team and assessment planning.
  • RMF
  • CMMC
  • NIST 800-171
  • Incident response
  • Nessus
  • KnowBe4
Visit WRA
2023 — 2025Part-time consulting
InFocus

Penetration Tester

InFocus Consulting

Feb 2023 — Feb 2025

Testing systems, networks, and web applications to turn exploitable weaknesses into clear, actionable remediation work.

  • Identified and helped remediate over 100 critical vulnerabilities across client engagements.
  • Delivered findings, impact analysis, and remediation recommendations in Dradis and PlexTrac.
View full role details5 areas of responsibility & technical workExpand

Penetration testing

Performed authorized penetration testing and exploitation of systems, target networks, and web applications using advanced testing methodologies.

Assessment tooling

Used Burp Suite and Qualys to discover, validate, and document network and application vulnerabilities.

Threat-informed planning

Developed exploitation-focused test plans based on threat intelligence and risks to client infrastructure.

Reporting & remediation

Produced comprehensive reports through Dradis and PlexTrac, and worked with developers and system administrators to resolve findings.

Continuous research

Maintained current knowledge of vulnerability advisories, incidents, exploitation techniques, and assessment best practices.

  • Penetration testing
  • Burp Suite
  • Qualys
  • Dradis
  • PlexTrac
2021 — 2024Security engineering

Cyber Security Engineer & Vulnerability Management

Lockheed Martin

Feb 2021 — Apr 2024

Building and hardening infrastructure, automating configuration, and connecting vulnerability intelligence with global remediation.

  • Configured Palo Alto Firewalls and applied DISA STIGs to network infrastructure.
  • Automated device configuration and administration with Ansible playbooks.
View full role details7 areas of responsibility & technical workExpand

Network engineering

Configured and deployed Palo Alto firewalls, applying DISA STIGs and knowledge of ports, protocols, and OSI-layer behavior to harden networks.

Monitoring infrastructure

Built and managed administrative virtual machines, including Identity Management and ELK stack instances, to improve visibility and system performance.

Configuration automation

Developed Ansible playbooks for device configuration and network and systems administration, supporting consistent compliance across enclaves.

Incident investigation

Supported incident response and forensic investigations with Arctic Wolf, including timeline reconstruction and technical findings for stakeholders and legal teams.

Vulnerability management

Validated HackerOne submissions, coordinated global remediation, and tracked findings in Jira.

Threat intelligence

Used Recorded Future and open-source intelligence to assess cyber threats and produce actionable reports for senior leadership.

Traffic analysis

Analyzed firewall and ELK telemetry to identify anomalous behavior, support metadata-driven analysis, and inform remediation and hardening.

  • Palo Alto
  • Ansible
  • ELK stack
  • HackerOne
  • Recorded Future
  • Jira
Visit Lockheed Martin
2019 — 2021Cyber intelligence

Intelligence & Network Exploitation Analyst

Booz Allen Hamilton

Mar 2019 — Feb 2021

Translating network, communications, and blockchain analysis into intelligence for DoD and law enforcement stakeholders.

  • Analyzed adversary infrastructure and target communications to support cyber operations planning.
  • Delivered intelligence reports and high-interest briefings to senior leadership.
View full role details4 areas of responsibility & technical workExpand

Digital network research

Conducted cyber intelligence and digital network exploitation research, including blockchain transaction investigations, to identify risks and target communications.

Infrastructure analysis

Profiled adversary infrastructure using open-source and classified sources to support intelligence requirements and operations planning.

Decision support

Delivered actionable intelligence and briefings for strategic planning, target development, and cybercrime prevention.

Metadata & continuity

Analyzed metadata, researched targets, and contributed to global network analysis and mapping to maintain target continuity.

  • Cyber intelligence
  • Network analysis
  • OSINT
  • Blockchain analysis
Visit Booz Allen
2013 — PresentMilitary service
Joint Special Operations Command emblemTennessee Air National Guard emblemUnited States Air Force symbolCurrent role

Military Service

U.S. Army Special Operations Command & Tennessee Air National Guard

Aug 2013 — Present

A foundation in mission support, signals intelligence, and technical problem-solving, spanning network analysis and an early career in aircraft avionics.

  • Provided round-the-clock SIGINT and cyber intelligence support to special operations missions.
  • Produced actionable intelligence and briefings to support leadership and mission planning.
View full role details6 areas of responsibility & technical workExpand

Mission support

Provided 24/7 signals intelligence and cyber intelligence support, including analysis and mapping of adversary digital communications and network infrastructure.

Assessment support

Supported red-team efforts and Computer Network Exploitation operations to identify vulnerabilities and enhance mission effectiveness.

Network intelligence

Analyzed SIGINT and cybersecurity data across the OSI stack and delivered actionable intelligence products and high-interest briefings.

Technology research

Researched target technologies, digital communications, and network topology to support access and exploitation analysis.

Analytical continuity

Analyzed collection and open-source data to profile target activity, maintain continuity, and develop additional cyberspace information.

Technical foundation

Performed troubleshooting, preventive maintenance, and calibration of military aircraft avionics in an early-career technical role.

  • SIGINT
  • Target network analysis
  • CNE support
  • Avionics

Tools & technologies

The tools behind
the work.

A practical toolkit spanning assessment, engineering, monitoring, intelligence, and reporting.

  • Assess

    Nessus

    Enterprise vulnerability analysis and remediation prioritization.

  • Assess

    Burp Suite

    Web application testing, vulnerability validation, and exploitation.

  • Assess

    Qualys

    Scanning and assessment of network and application security.

  • Assess

    HackerOne

    Submission validation and coordinated vulnerability remediation.

  • Monitor

    Splunk

    Centralized telemetry and security monitoring across enclaves.

  • Monitor

    Arctic Wolf

    Threat monitoring, incident response, and forensic coordination.

  • Monitor

    Palo Alto Cortex

    Threat monitoring and incident detection across enterprise environments.

  • Monitor

    Windows Defender

    Endpoint protection within enterprise detection and response workflows.

  • Monitor

    ELK stack

    Log infrastructure, network visibility, and telemetry analysis.

  • Intelligence

    Recorded Future

    Threat intelligence research and reporting for leadership decisions.

  • Engineer

    Ansible

    Automated configuration, administration, and compliance consistency.

  • Engineer

    Palo Alto Firewalls

    Network infrastructure deployment, hardening, and traffic analysis.

  • Engineer

    SCAP benchmarks

    Configuration assessment against defined security benchmarks.

  • Document

    Dradis

    Structured assessment findings, impact, and remediation reporting.

  • Document

    PlexTrac

    Clear vulnerability reports and actionable remediation recommendations.

  • Document

    Jira

    Tracking security findings and coordinated remediation work.

  • Document

    KnowBe4

    Security awareness campaigns across a 1,100+ user organization.

  • GRC

    IntelliGRC

    Governance, risk, and compliance tooling for control and evidence management.

  • GRC

    FutureFeed

    GRC tooling supporting NIST 800-171 and CMMC compliance workflows.

  • GRC

    eMASS

    Enterprise mission assurance tooling for RMF documentation and authorization workflows.

Tools are shown in the context of my experience. Select a tool name to visit its official website.

Education & credentials

A technical foundation.
A commitment to learning.

Industry certifications, specialized military training, and continuing study in cybersecurity and information assurance.

Specialized training

Military courses

Formal training from intelligence fundamentals and cyber analysis to electronics and avionics.

  1. 2016

    Joint Cyber Analysis Course

    Department of the Navy

    JCAC
  2. 2015

    Digital Network Intelligence Analysis Apprentice Course

    Community College of the Air Force

    Network intelligence
  3. 2015

    Intelligence Fundamentals Course

    Community College of the Air Force

    Intelligence
  4. 2011

    Avionics Technician — Heavies

    Community College of the Air Force

    Avionics
  5. 2011

    Electronics Principles Course

    Community College of the Air Force

    Electronics

Get in touch

Let’s start
a conversation.

For professional opportunities and conversations about cybersecurity, engineering, and intelligence.

⌖ Draper, Utah